Synology DSM
Use Container Manager → Project on a DSM model that supports Container Manager. Basic runs on the NAS. For GPU or Full, use a separate NVIDIA machine and enter its private address in GPU box address below. Full also needs a reader. If those services already run in Kubernetes or on another host, use the existing-service settings. Requirements covers memory and storage.
Tested deployments says which Synology routes were run end to end.
1. Create a project
-
Open Container Manager → Project → Create and name the project
immich-memories. -
Click Set Path, select your
dockershared folder, then Create Folder. Name the folderimmich-memories, click OK, select the new folder and click Select.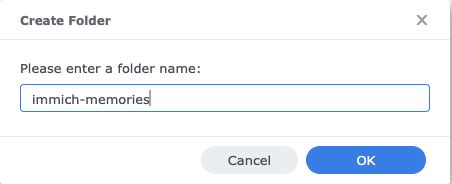
-
Set Source to Create docker-compose.yml. This opens the editor.
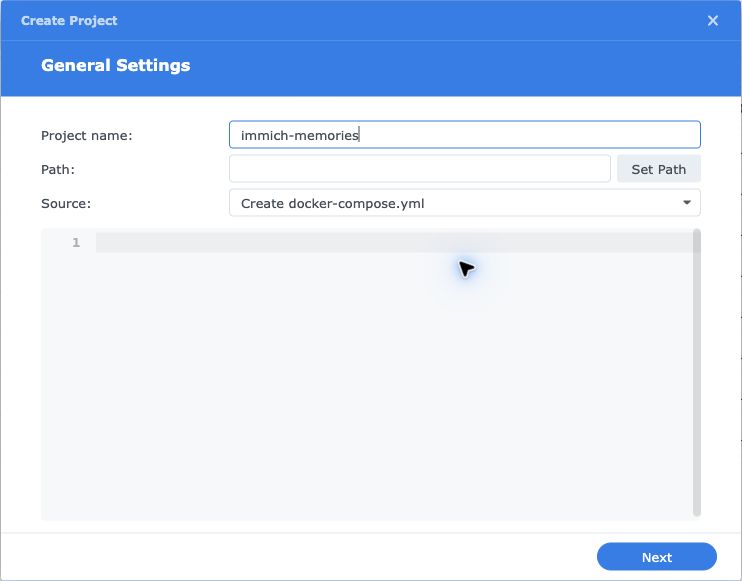
Choose your tier below. Enter the Immich URL the NAS can reach, copy docker-compose.yml into
the editor, and replace replace-with-your-immich-api-key with your
Immich API key. For Full, also replace the reader key placeholder,
or empty it for a reader without authentication.
This page runs entirely in your browser. What you type here is never sent anywhere: no requests, no analytics, no tracking. The files are built on this page and stay on it until you copy or download them.
Setup files for docs build v1.0.0. The app image and release assets use this same version.
The builder does not ask for your Immich API key. The files hold the placeholder replace-with-your-immich-api-key: create a key with the ten required read permissions and paste it over the placeholder in your own editor. Add the five upload permissions only to send films back; asset.delete is optional. Avoid the All preset.
Platform coverage and tested installations
See the deployment matrix for exact release and platform coverage.
Not yet tested as an end-to-end generated installation on Synology Container Manager. Files are checked with Compose and the form is checked in a browser. Those checks do not run this installation. Earlier NAS, Mac and GPU Kubernetes checks are recorded in the measured results. Tried it? Report your platform, release and preflight result.
Nothing here contacts an Immich or model server.
Generate a private settings key before exporting a single-file stack.
Keep Single file for a stack editor selected. The generated file includes a Settings encryption key; keep it with your backups and restrict access after adding your API keys.
Docker-managed volumes retain settings, prepared facts and films across container replacement. Download films through the app. To use a NAS share instead, follow folder permissions before changing the output mount.
Keep the saved file private using File Station → Properties → Permission. It contains keys.
2. Choose access and start
The app asks for a sign-in either way. To open it to your trusted LAN, tick Open the UI to
other machines on my LAN in the builder above. Leave the login empty to get a generated password
(read it with docker logs immich-memories or in the container's log view), or enter a username
and a password of at least 12 characters and the generated file carries them.
To do it by hand, edit the lines the file already has. Do not add a second copy: Compose refuses a
file that defines the same key twice. To pick your own login, change the two empty values under the
app service's environment: block:
IMMICH_MEMORIES_AUTH_USERNAME: admin
IMMICH_MEMORIES_AUTH_PASSWORD: replace-with-your-own-long-password
The password needs at least 12 characters. To publish the port, in the same service's ports: change
127.0.0.1:22830:8080 to 0.0.0.0:22830:8080. If the host already uses 22830, choose another host
port, for example 0.0.0.0:22831:8080. The last number remains 8080.
This is the app's login; the container manager's account does not protect this port. These settings use HTTP on your LAN. For HTTPS or private access through localhost, use the other access routes.
Finish the wizard and start the project. No Web Station portal is needed. For a new separate GPU worker, run the generated GPU-host commands there first; keep its model service port accessible only from your app host on your private network. Skip those commands when reusing existing services.
3. Open the app and download models
Open http://your-nas-address:22830 (or your chosen host port) and sign in with the
login you set, or with the generated password from the container's log in Container Manager. With
private localhost access, use the forwarded URL instead.
On Memory, click Download models and wait for it to finish. The card lists the files and download hosts; it disappears when the required files are ready. If it is absent and no error is shown, those files are already present. Downloads are kept on the config volume for later starts.
4. Check and make a film
Basic: continue to your first film.
GPU and Full: the browser download does not check the external model services. In Container Manager, open a /bin/sh terminal in the running immich-memories container.
Run:
immich-memories preflight
This runs inside the app container, so do not add docker exec. Wait for inference and captions
(and the Full reader) to become ready, and resolve any required-service or storage errors before
making your first film. Optional upload permissions can warn
while still allowing local films.
Installation help covers connection, port, permission and startup errors. It also gives the CLI model-download command if you need it.
Other access routes and troubleshooting
Synology access and troubleshooting covers an HTTPS reverse proxy, forwarding restrictions and a release-file installation over SSH. Installation help covers readiness errors.